

ISO 31000:2018 provides guidelines for managing risk across an organization. It can be adapted to different activities and sectors. It is not an information security management system certification standard. ISO 31000:2018
Apply the risk management process
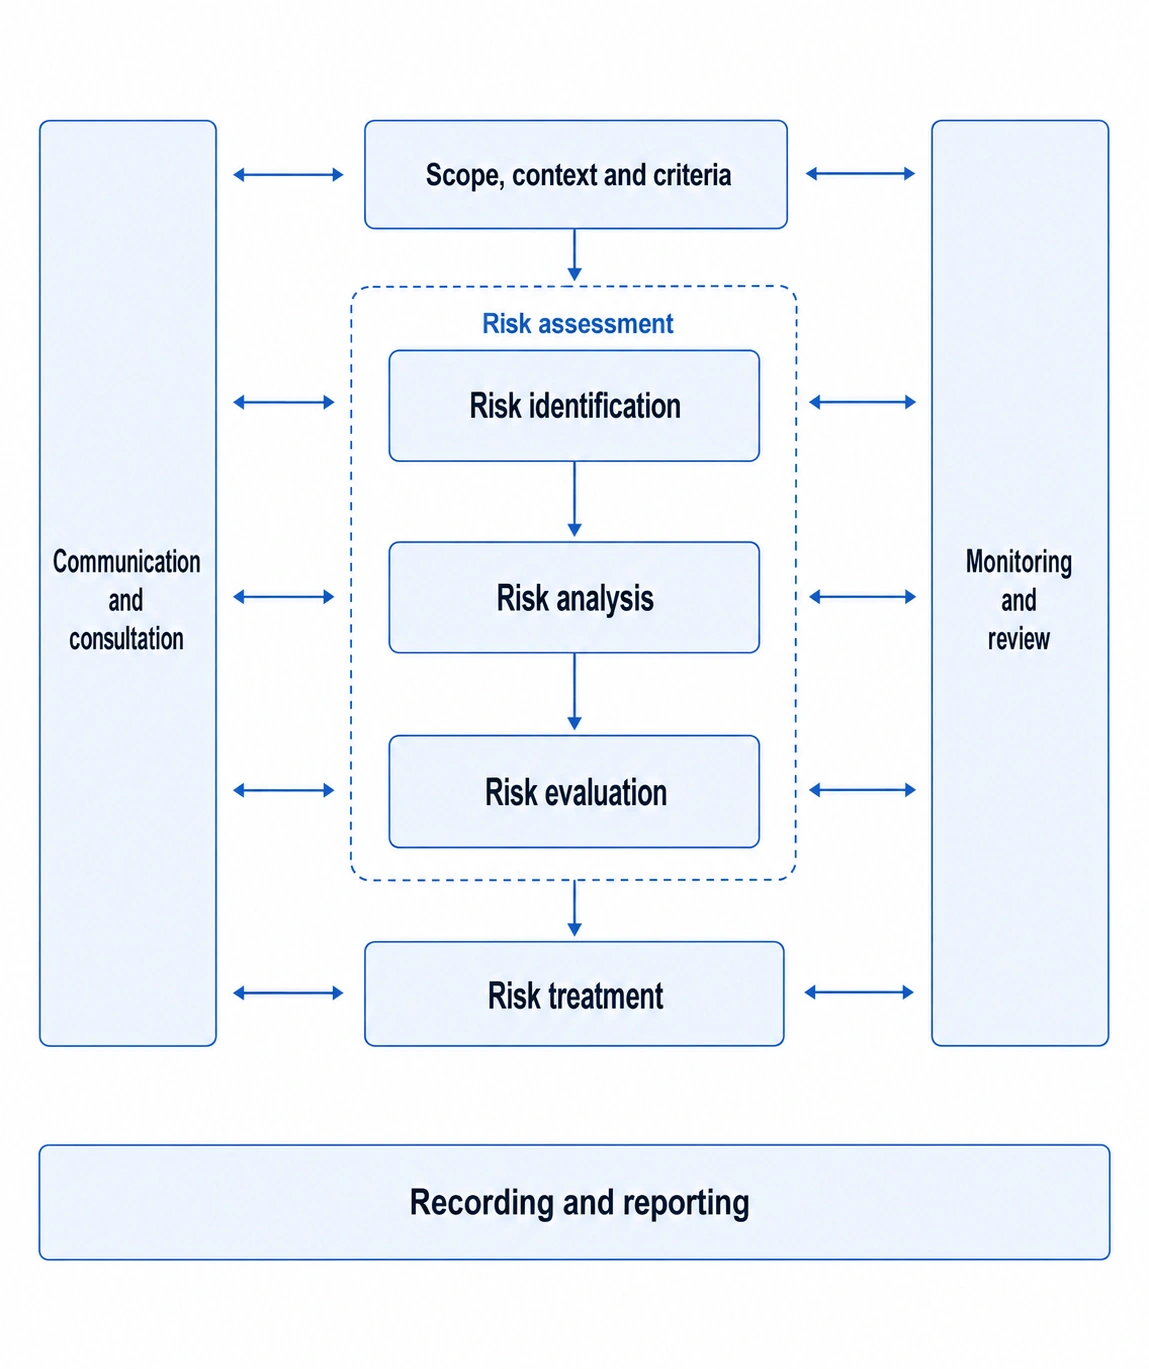
Establish the scope, context and criteria for the decision. Identify the relevant risks, analyse their characteristics and evaluate them against those criteria. Select and implement suitable treatment, then monitor and review the results.
Communication, consultation, recording and reporting support the process. Revisit the assessment when objectives, assumptions or circumstances change.
Relate it to continual improvement
Plan–Do–Check–Act is a useful way to discuss planning, implementation, review and improvement. It should not replace ISO 31000's own process terminology or be presented as its four mandatory stages.
For requirements covering an information security management system, refer to ISO/IEC 27001. The standards have related uses but different scopes. ISO/IEC 27001
Use the edition applicable to your organization's work, and check clause references against that edition. Clause numbers from an older edition should not be relabelled as ISO 31000:2018.