

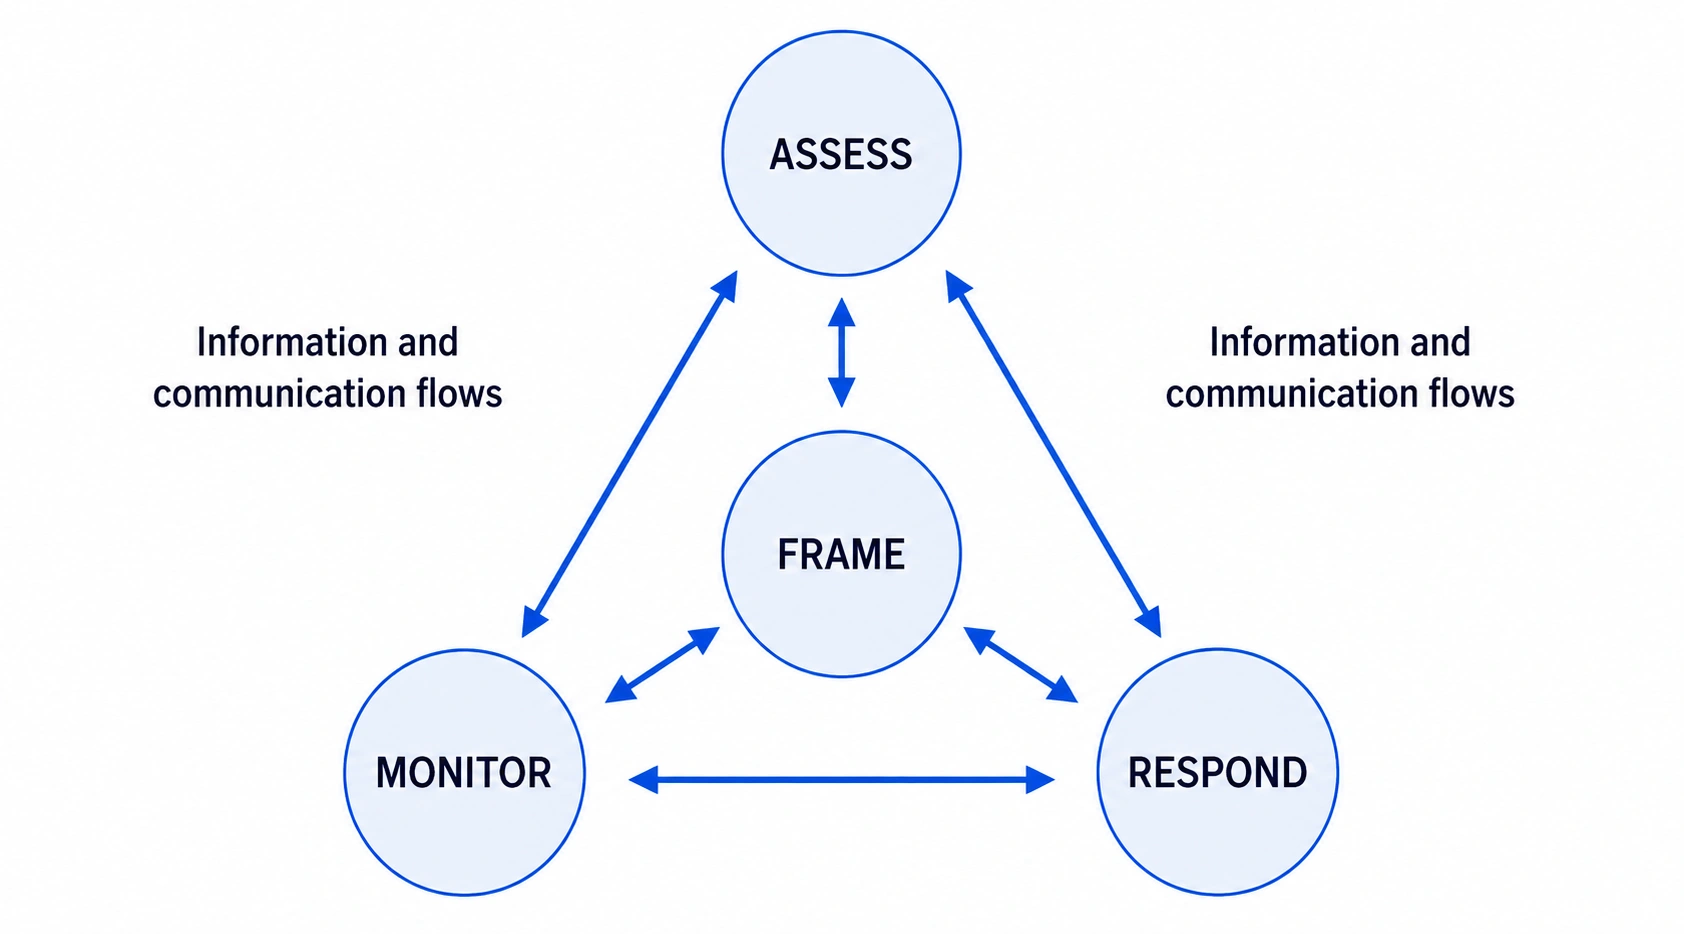
NIST SP 800-39 describes four connected components of risk management. Information flows between them as the organisation's context, assessments and responses change. Treat them as an ongoing process, rather than four tasks completed once.
Frame risk
Establish the context, assumptions, constraints and risk tolerance that guide decisions. Define how the organisation will assess, respond to and monitor risk.
Assess risk
Identify and analyse risk in that context, considering threats, vulnerabilities, likelihood and potential impacts. Record uncertainty and the evidence supporting the assessment.
Respond to risk
Evaluate possible responses, select an appropriate course of action and implement it. The response should reflect the organisation's objectives, constraints and tolerance.
Monitor risk
Review changes in the environment and the effectiveness of the selected responses. Feed the findings back into framing, assessment and response decisions.