

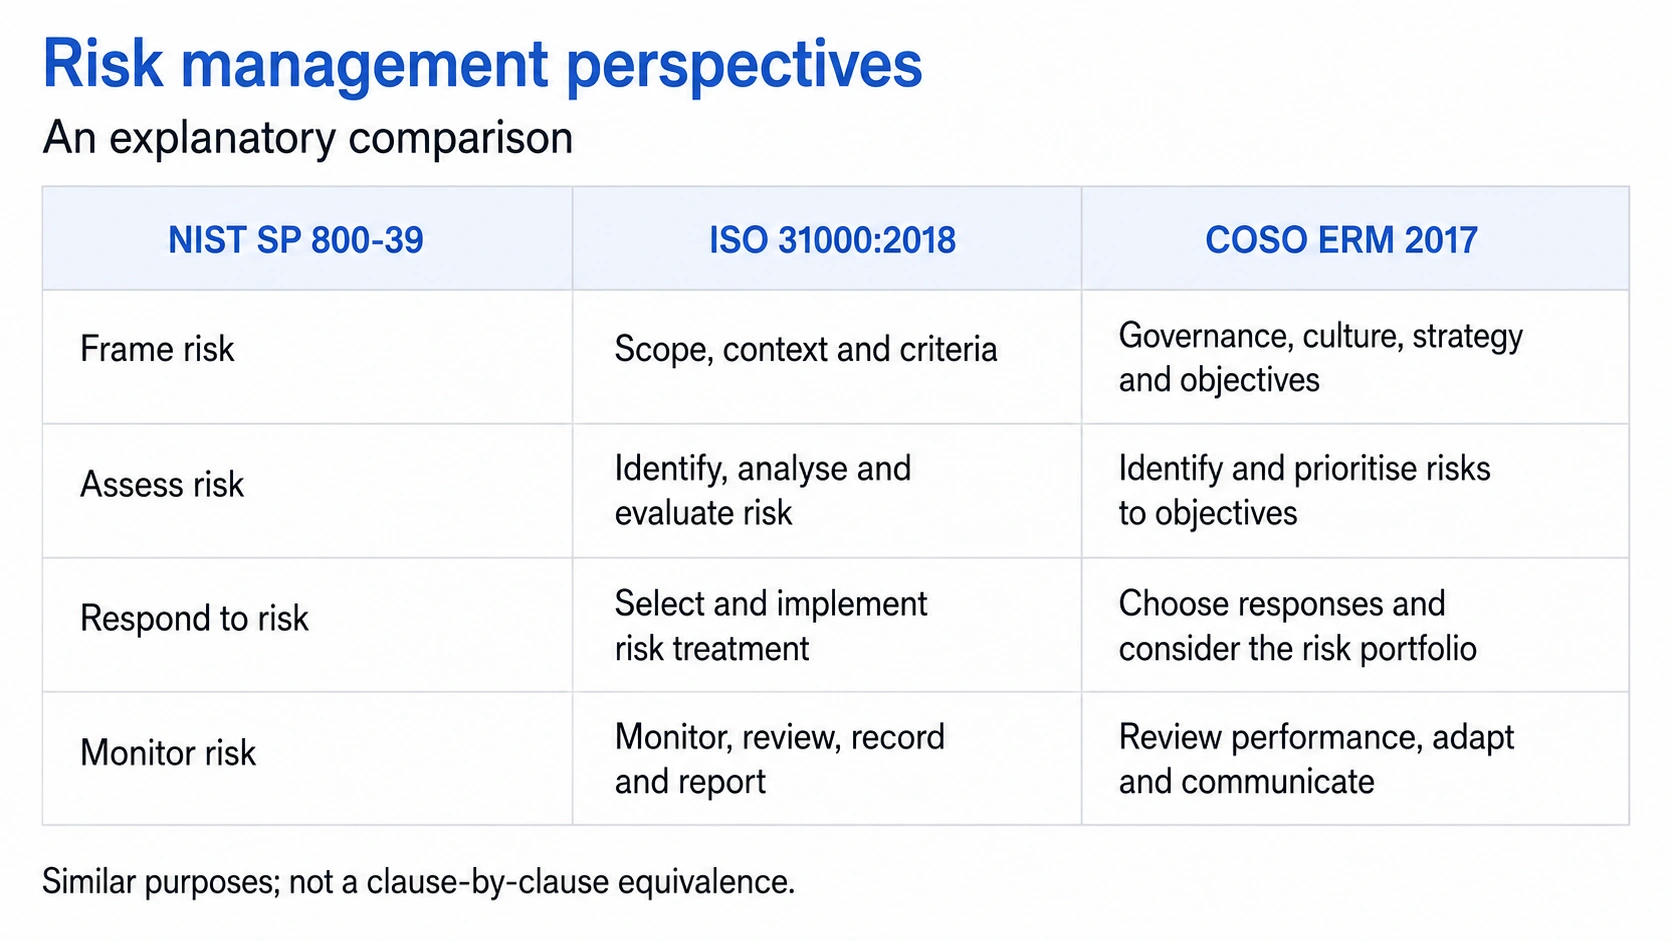
The following comparison helps readers recognize related risk management activities across three publications. It is an editorial explanation, not an official crosswalk or evidence that applying one publication satisfies another.
| NIST SP 800-39 | ISO 31000:2018 | COSO ERM 2017 |
|---|---|---|
| Frame risk | Scope, context and criteria | Governance, culture, strategy and objectives |
| Assess risk | Identify, analyse and evaluate risk | Identify and prioritise risks to objectives |
| Respond to risk | Select and implement risk treatment | Choose responses and consider the risk portfolio |
| Monitor risk | Monitor, review, record and report | Review performance, adapt and communicate |
The activities overlap and inform each other. Read the table as a comparison of purposes; the rows are not a required sequence or a clause-by-clause equivalence.
NIST SP 800-39 addresses information security risk across the organization, mission or business process, and information system levels. NIST publication
ISO 31000 provides general risk management guidelines. Its scope differs from the ISMS requirements in ISO/IEC 27001. ISO publication
COSO's 2017 ERM framework connects risk with strategy and performance. Its governance and information-related themes support the work throughout; they are not confined to one row of this table. COSO ERM framework