

The CSFaaS Risk Management solution is a comprehensive, adaptable set of modules for managing cybersecurity risk. It keeps risk work aligned with business objectives, improves risk visibility, and strengthens governance.
1. Key features
Framing your environment
Define the vocabulary of your risk process (risk categories, threat actors, impact types, priorities and more) in workspace catalogues, so every assessment is described in consistent, comparable terms.
Risk demand management
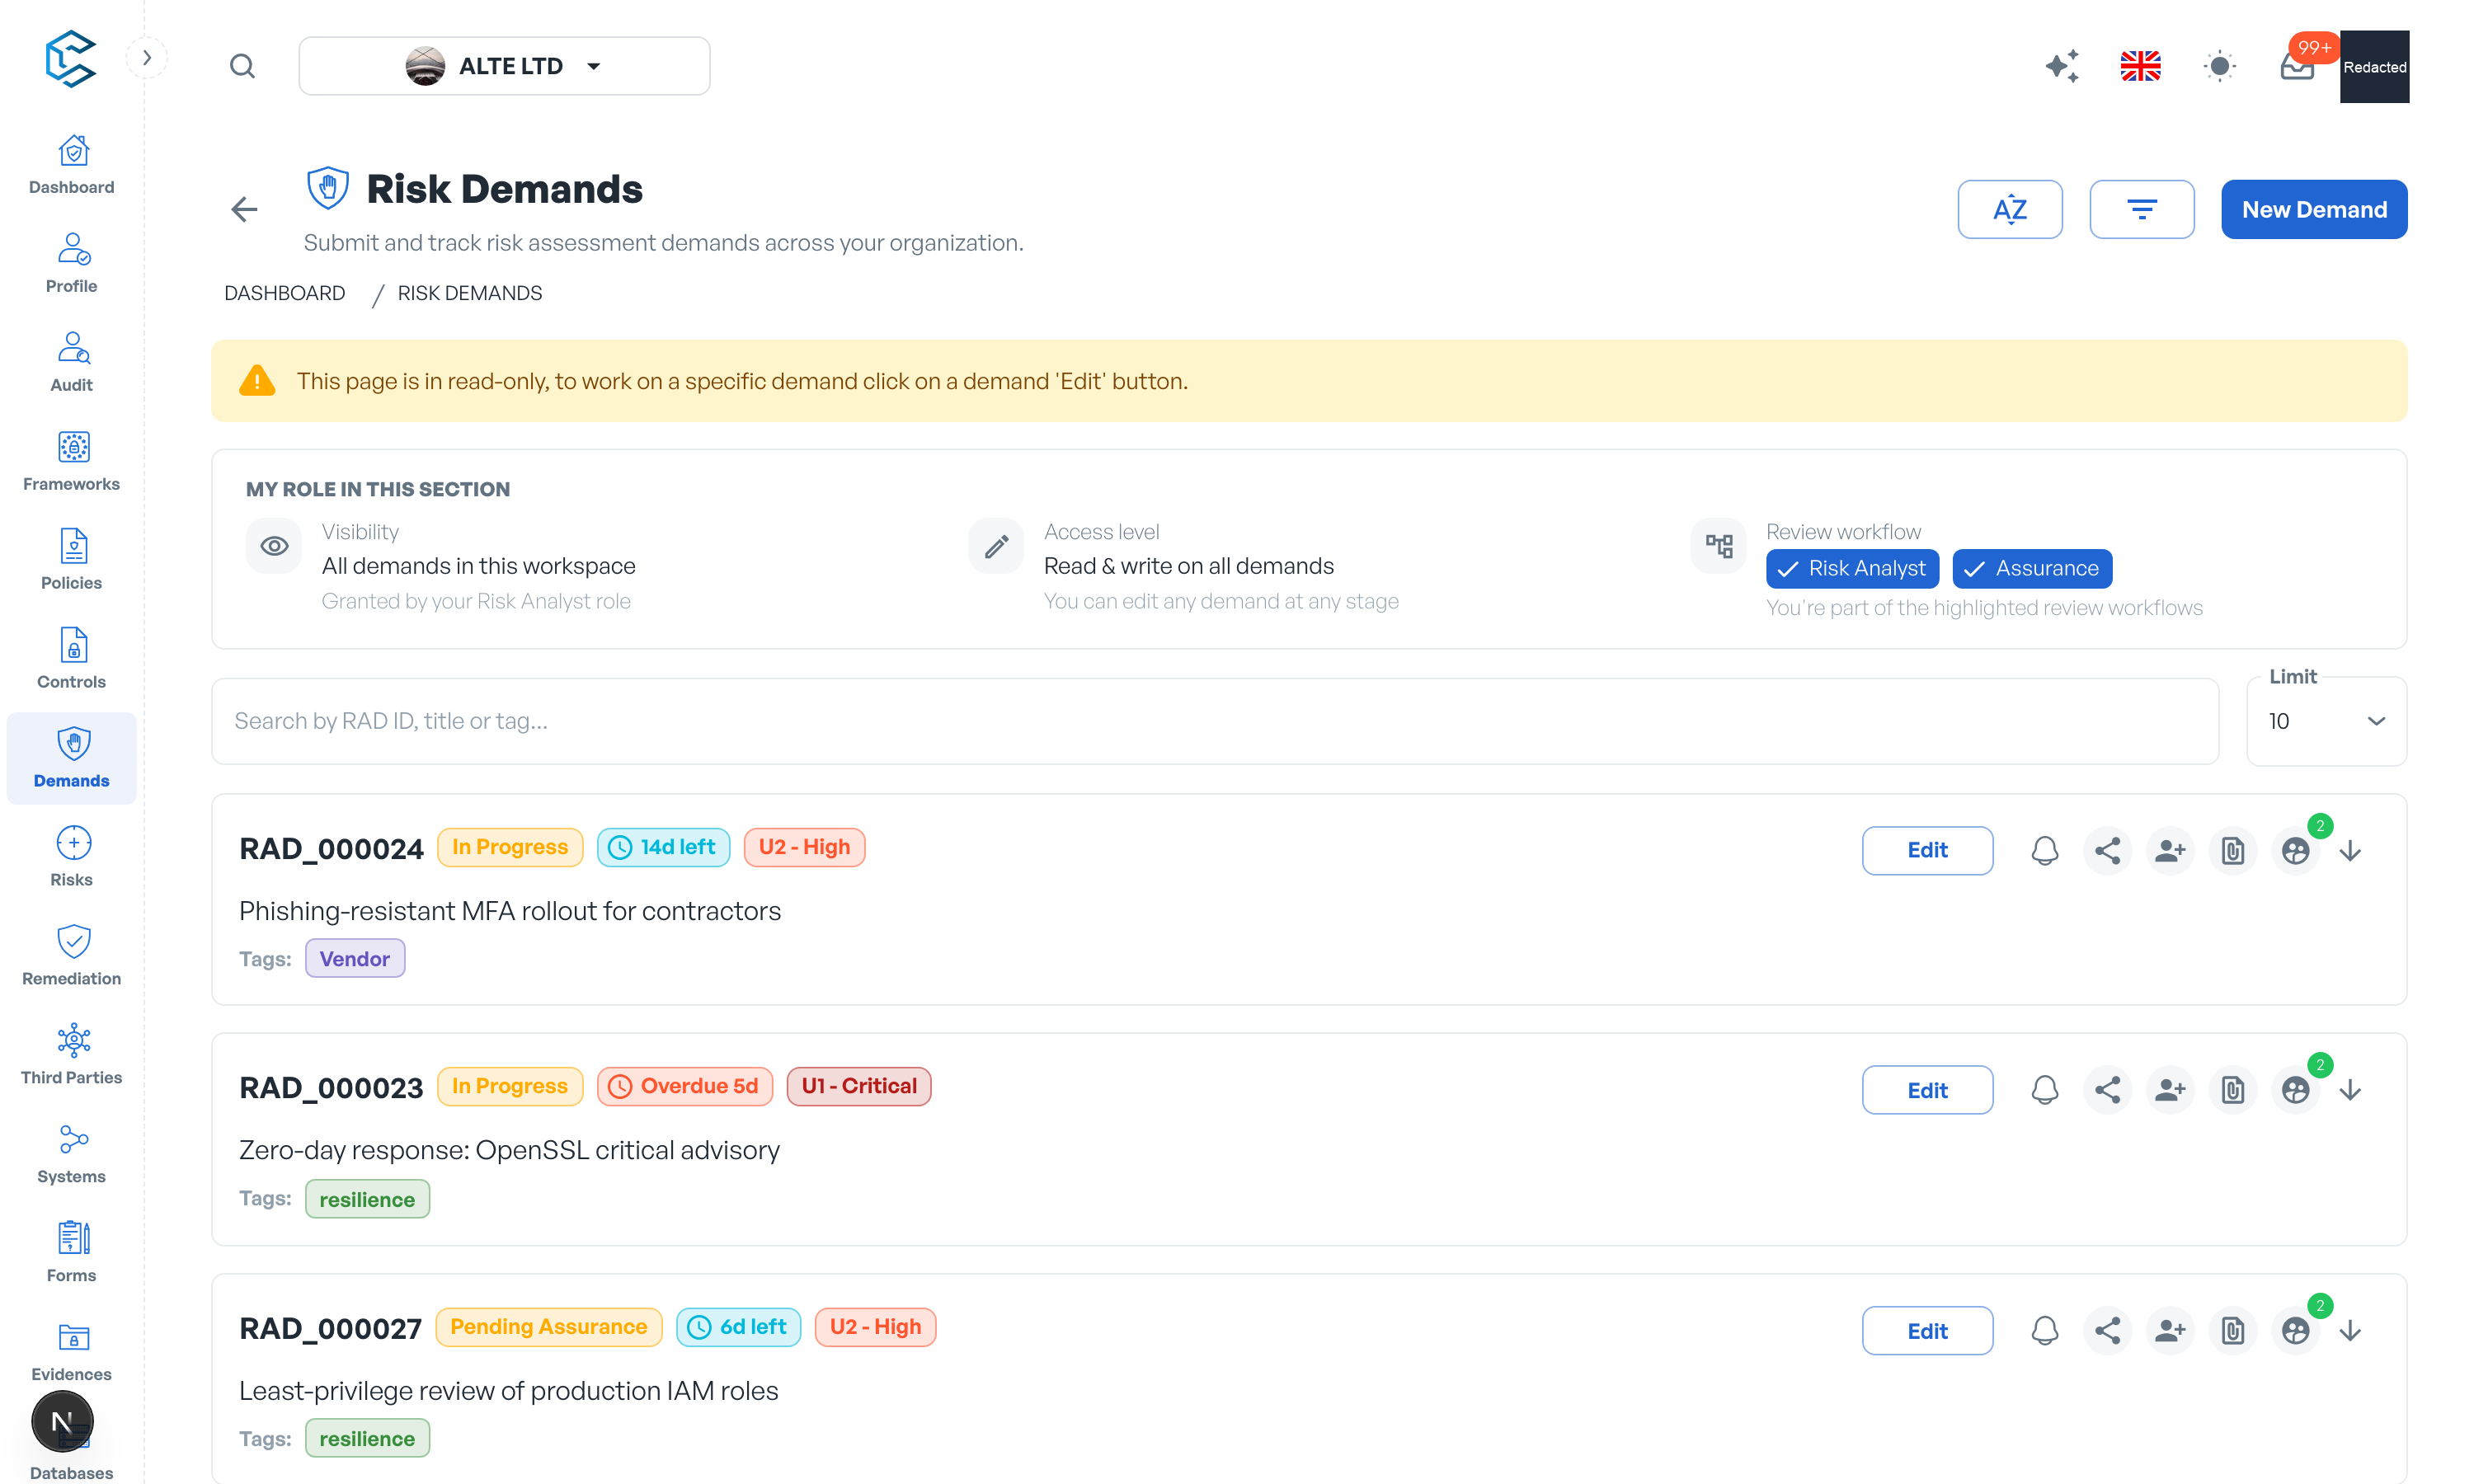
Anyone in the workspace can raise a risk assessment demand. A demand starts as a quiet draft, is submitted for review, and then moves through a tracked workflow to completion. The status chip on each demand opens the Demand Status drawer: a timeline of every status change, who made it and when, plus the actions available to you at the current stage.
Risk lifecycle management
Each demand carries its risk assessments: profile the threat, score inherent, current and target risk on your risk matrix, recommend controls and record the risk response. Every risk is automatically registered in the Risk Registry, the central record of identified risks.
Remediation plan tracking
Mitigation decisions become remediation plans with a responsible person, a due date with an SLA countdown, and a validated completion flow, tracked centrally in the Remediation Plans module.
2. Support features
Collaboration and documentation
Comment on demands, risks and remediation plans, follow their activity feeds, and invite workspace members as stakeholders on a specific demand so they can collaborate without broader risk permissions.
Evidence management
Attach supporting files or links at demand, risk and remediation-plan level to substantiate assessments and decisions.
Analytics and visualisation
Each demand renders a flow diagram linking the demand to its risks and remediation plans. The Risk Registry adds a risk responses overview, interactive current and target risk matrices, and distribution charts by threat taxonomy.
Workflow and approvals
Optionally enforce a review workflow: an Analyst triages each demand, the requester provides the risk response, approvals can require one or every analyst, and an Assurance reviewer can hold the final gate before completion. Every transition asks for confirmation and is recorded in the demand timeline.
By combining these features, your organisation can proactively manage cybersecurity risks, enhance compliance, and streamline risk governance. The following sections walk through each capability in detail.
Privacy note. Personal details in this revision have been removed, masked or replaced for privacy. The original is retained privately.